
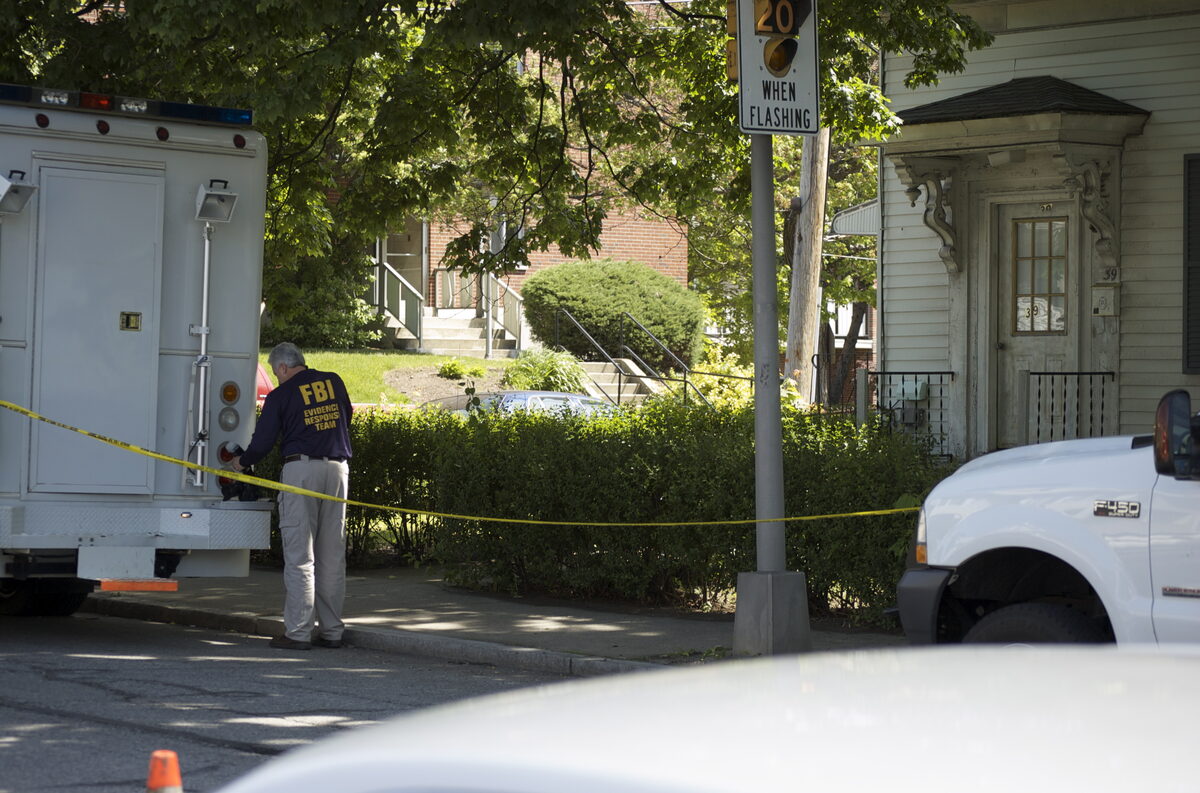
On October 13, the Justice Department announced a set of coordinated actions against North Korean remote IT-worker schemes. They include a 14-defendant federal indictment in Ohio and a multi-day FBI search operation in Texas called "Operation Lonestar Roundup." On the same day, the FBI published a public service announcement warning that these workers are expanding their use of facilitators, broadening recruitment and changing how they operate.
The indictment: 14 defendants, four counts
According to the DOJ press release, a four-count indictment in the Northern District of Ohio charges wire fraud, money laundering and identity theft. It names 14 defendants:
- Two US nationals, who have been arrested: Michael James Bostelle of Pennsylvania and Juan Cecilio Pena Carrillo of Texas;
- Ten individuals based in China; and
- Two defendants whose identities remain under seal.
DOJ says the scheme ran from 2019 until about July 2025. Prosecutors allege it used stolen or fabricated identities, VPNs and proxies, and US-based "laptop farm" facilitators who hosted company laptops and moved earnings to accounts controlled by North Korea. DOJ says the workers were placed with more than 70 US companies in health care, communications, cyber support, retail and manufacturing, located in Ohio, sixteen other states and the District of Columbia. According to DOJ, the scheme generated about $3 million.
DOJ also published eleven fraudulent email accounts tied to the scheme as indicators. Assistant Attorney General for National Security John A. Eisenberg said in the announcement that "North Korea's rogue regime uses its pervasive IT worker schemes to raise revenue for various illicit purposes." U.S. Attorney David M. Toepfer of the Northern District of Ohio called the charges "an urgent alert to all U.S. companies to remain vigilant in their hiring practices." The release also notes that the State Department has offered rewards of up to $5 million for information on North Korean illicit financial activities. DOJ stresses that the charges are allegations. All defendants are presumed innocent until proven guilty.
Operation Lonestar Roundup
The second part of the announcement concerns hardware. According to DOJ, FBI agents searched more than 40 residences in Texas between September 21 and 25 and seized about 187 laptops and keyboard-video-mouse (KVM) devices.
These are the "laptop farms" behind remote IT-worker fraud. An employer ships a company laptop to what it believes is a new hire's home address. The device ends up in a US residence run by a facilitator, and the overseas worker works on it remotely. To the employer's network, the traffic looks like it comes from a domestic residential connection.
BleepingComputer, reporting on the raids on October 14, cited CrowdStrike, which says it assisted the FBI. CrowdStrike tracks the operators as Famous Chollima (also known as WageMole) and has followed them since April 2025. CrowdStrike expects actions like this to have limited impact, but called the Texas searches "the beginning of a broader U.S. law enforcement effort to dismantle Famous Chollima's U.S. infrastructure." CrowdStrike also described four ways the operators get corporate devices to laptop farms. They file fake theft reports so replacement hardware is shipped. They rotate residential addresses. They claim last-minute relocations to divert shipments. They also abuse IT staffing roles to redirect shipments. Nextgov/FCW also reported more than 40 searches and about 187 devices. It cited CrowdStrike as saying the campaign targeted more than 70 US companies.
What the FBI says has changed
The companion advisory, FBI PSA I-101326-PSA, is titled "North Korean IT Workers Expanding Use of Facilitators, Broadening Recruitment." It describes these changes:
- More facilitators. The FBI says dozens of North Korean IT-worker teams are hiring Americans and others for a wider range of facilitation tasks.
- Smaller, more numerous laptop farms. The workers now run more farms with fewer laptops at each, "to avoid single points of failure."
- Subcontracting. Work is subcontracted to freelancers "usually in Pakistan, India, Nigeria, or neighboring countries."
- Threats. The FBI says that after being fired, the workers have made death threats against former managers and their families.
- Cleared positions. The workers target positions with cleared defense contractors and other firms that hold US government contracts.
- Impersonation. Operators falsely claim accounts and identities that belong to other people, including profiles on professional networking sites.
- Military recruitment. The FBI says the workers target active-duty US military members to host laptops.
The Texas operation, with dozens of residences and fewer than five devices per site on average, appears consistent with the distributed laptop-farm model the PSA describes.
What It Means for Defenders
The FBI's main recommendation is what it calls "identity in depth." It says these workers "cannot be identified reliably with a single indicator," so detection should use layered controls across the whole employment lifecycle. Based on the PSA and the reporting above, practical steps include:
- Check the published indicators. Search applicant tracking systems, HR records and mail logs for the eleven fraudulent email accounts listed in the DOJ release. A match should start a review of that worker's access, payroll records and device custody.
- Watch for remote-desktop tools. The PSA says the workers "continue to use remote desktop software to connect to employment-related devices," and that they "almost always exfiltrate data," often through screen recordings. Endpoint and network monitoring should alert on remote-desktop tools outside the approved list, especially on newly issued laptops.
- Treat KVM hardware as a signal. The FBI seized laptops alongside KVM-over-IP hardware, which the PSA lists (TinyPilot, PiKVM, GL.iNet) as a way these workers control company devices. Where endpoint tooling can see attached peripherals, unexpected KVM hardware on corporate laptops deserves investigation.
- Flag identifier churn and shipping changes. The PSA warns that the workers tend to rotate through bank accounts, street addresses, social media accounts and other identifiers at unusually high rates. CrowdStrike's description of fake theft reports, rotating addresses and last-minute relocations points the same way. Device replacement requests and shipping-address changes should go through security review, not only IT or facilities.
- Add friction to identity verification. The FBI says E-Verify, requiring a US passport, multiple forms of identification, or live verification can make things harder for these workers. Because operators now impersonate real professionals, a candidate whose public profile looks legitimate can still be someone else.
- Get HR, IT and security working together. The PSA says cross-functional collaboration between internal teams improves detection, and that IT, HR, security and management should share what they see. Often each team holds part of the picture: HR has the address change, IT has the replacement laptop, and security has the unusual remote session.
- Review cleared and contracted roles. The PSA says positions at cleared defense contractors are being targeted and that work is subcontracted. Organizations in those categories should check how staffing-agency placements and contractor identities are verified.
- Avoid blunt filters. The FBI cautions that relying only on ban lists or name filtering is unreliable and can harm qualified applicants and identity-theft victims. It also warns that aggressive controls carry an unusually high risk of false positives.
- Plan for threats. Given the FBI's warning about death threats against former managers, removing a suspected worker should involve legal and security planning, not just turning off accounts.
- Report it. The FBI asks people to report suspected North Korean IT-worker contact to their local FBI field office and through an IC3 complaint at ic3.gov.
What comes next
The case against the two arrested US nationals will proceed in the Northern District of Ohio. DOJ has not identified the two sealed defendants. CrowdStrike has said it sees the Texas searches as the start of a broader effort against the group's US infrastructure.
For employers, the FBI's advisory may matter more than the indictment. It describes operators spreading hardware across smaller farms, subcontracting work and taking over real people's identities. Under that model, detection depends on the layered, cross-team checks the FBI recommends.
Sources
- U.S. Department of Justice: Justice Department Announces Coordinated Actions to Combat North Korean Remote IT Worker Schemes (Press Release 26-1171)
- FBI / IC3: PSA I-101326-PSA, North Korean IT Workers Expanding Use of Facilitators, Broadening Recruitment
- BleepingComputer: FBI raids DPRK IT worker laptop farms in Texas, US nationals arrested
- Nextgov/FCW: FBI disrupts North Korean 'laptop farm' used to infiltrate US companies
